
Build it right — on a fixed scope, fixed timeline
We design, migrate, modernize, and secure your Google Cloud environment as fixed-scope engagements. No open-ended consulting — named deliverables, stated timelines.
Your Google Cloud foundation: secure, compliant, ready in weeks
A production-ready landing zone — identity, network, security, and governance — built to NCA, SAMA, and PDPL, and handed over ready to build on.
You can’t retrofit a foundation. Teams that start building on Google Cloud before the landing zone is right pay for it later — in rework, security gaps, and failed audits. Identity, network, security, and governance are the parts you have to get right first.
Environment. Identity & access (IAM), network architecture, security baseline, logging & monitoring, IaC library, governance guardrails.
Handover. Technical Design Document, architecture diagrams, IaC module library, knowledge transfer, PDPL / ECC-2 / SAMA compliance report.
PACKAGES
| Included | Small / Foundation Start | Medium / Standard Enterprise | Large / Advanced Controls | X-Large / Strategic Scale |
|---|---|---|---|---|
| Identity & IAM | Included | Included | Included | Included |
| Logging & Monitoring | Included | Included | Included | Included |
| Infrastructure-as-Code | Included | Included | Included | Included |
| Security Baseline | Included | Included | Included | Included |
| Project Factory | Not included | Included | Included | Included |
| Identity Federation | Not included | Included | Included | Included |
| Network / TLS Inspection | Not included | Not included | Included | Included |
| Advanced Org Policies | Not included | Not included | Included | Included |
| External SIEM | Not included | Not included | Included | Included |
| Multi-Tenancy | Not included | Not included | Not included | Included |
| Dedicated Architect | Not included | Not included | Not included | Included |
Feature availability shown per package is indicative.
- + GCVE
- + GKE
- + CI/CD
- + NGFW
- + Secure Web Proxy
- + Data Platform
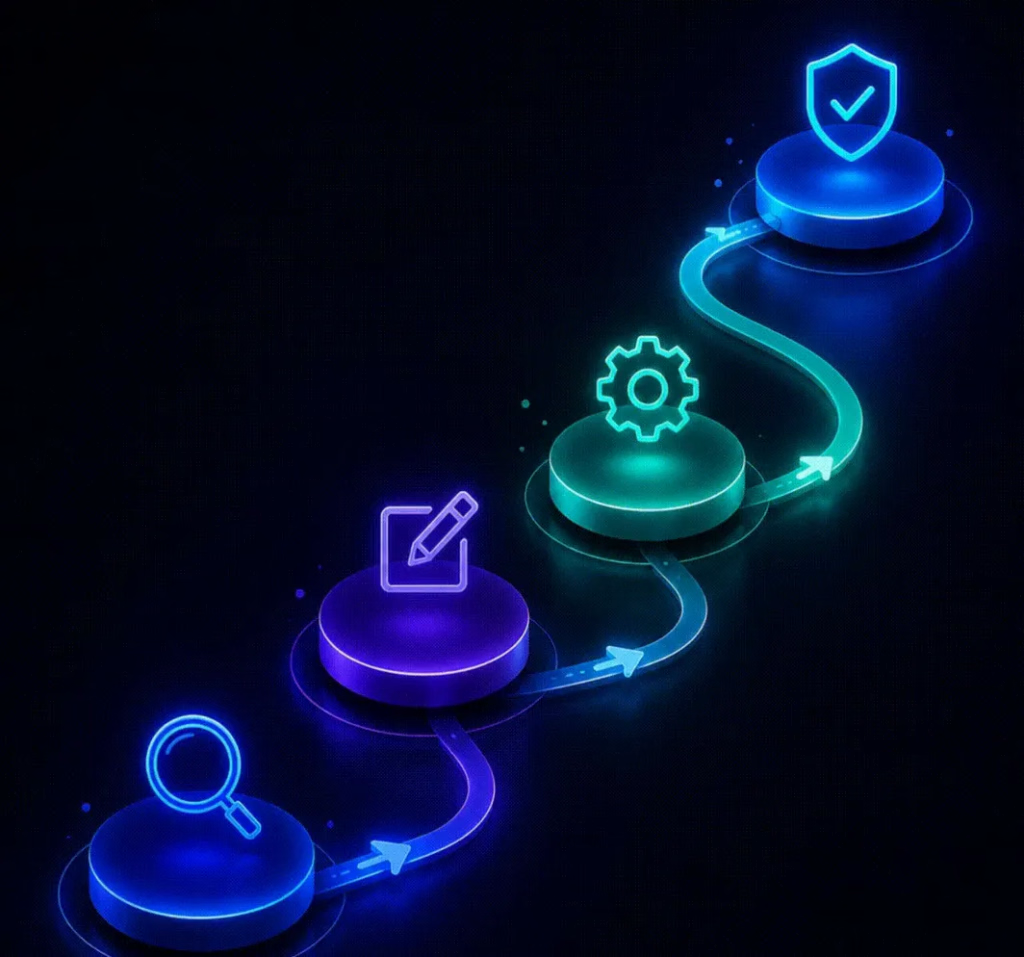
TIMELINE — LIVE IN 6–12 WEEKS
-
1
Assess — Current-state review and readiness check.
-
2
Design — Target-state landing zone architecture.
-
3
Build — Environment stood up with IaC.
-
4
Harden — Security baseline and governance applied.
-
5
Hand over — Documentation, IaC library, and knowledge transfer.
Standardized, certified, audit-ready — built by GCP-certified engineers on a standardized IaC library.
Move to Google Cloud without moving the risk
A staged, fixed-scope migration to the Dammam region — with a clear cutover and rollback plan.
Legacy estates migrate badly when they’re lifted as-is. Undocumented dependencies, compliance gaps, and big-bang cutovers turn migrations into outages. The risk isn’t the destination — it’s the move.
- Migration assessment and wave plan.
- Dependency mapping.
- Landing-zone readiness.
- Staged migration in waves.
- Cutover and rollback plan.
- Post-migration validation.
- Small
- Medium
- Large
- X-Large
Packages sized by workload count and complexity — confirm durations against the Cloud Services deck.
Migrations planned and run by GCP-certified engineers, into an in-Kingdom, compliant foundation.
Modernization, advisory, and security — built to the same standard
Application Modernization & GKE
Re-platform and refactor onto containers and Google Kubernetes Engine — so applications scale, ship faster, and cost less to run. Legacy applications are slow to change, expensive to run, and hard to secure; they hold back everything built around them.
- Modernization assessment.
- Containerization & GKE deployment.
- CI/CD pipelines & observability.
Cloud Advisory & Architecture
Independent assessment and target-state design — so the build starts from a decision, not a guess. Most cloud cost and risk is decided at the architecture stage, long before anyone notices.
- Current-state assessment.
- Target-state architecture.
- Cost & performance optimization.
- AI-readiness review & prioritized roadmap.
Security, Governance & Compliance
Baseline security, governance guardrails, and a 24/7 managed SecOps tier — aligned to NCA, SAMA, and PDPL. Security bolted on after the build is security with gaps; in regulated Saudi sectors, those gaps are the difference between passing an audit and failing one.
- Security baseline.
- Governance & org policies.
- Compliance mapping — NCA ECC, SAMA, PDPL.
- Managed SecOps — 24/7 SOC, SIEM/SOAR, CSPM.
- NCA ECC
- SAMA
- PDPL
Scope your engagement. See exactly what you’ll get, and when
Fixed scope, named deliverables, stated timeline — on an in-Kingdom, compliant Google Cloud foundation.